Data Encryption Standard (DES): Complete Explanation | Importance Of DES In Cryptography Education
Category: CRYPTOGRAPHY | 5th October 2026, Monday
Introduction To DES
The Data Encryption Standard (DES) Is A Symmetric-key Block Cipher That Was Historically One Of The Most Widely Used Encryption Algorithms. It Was Designed To Protect Digital Information From Unauthorized Access By Transforming Readable Plaintext Into Unintelligible Ciphertext. DES Uses The Same Secret Key For Both Encryption And Decryption. Although DES Is Now Considered Insecure For Modern Applications Because Its Key Size Is Too Small, It Remains Extremely Important In Cryptography Education Because Many Modern Encryption Concepts Can Be Understood Through Its Architecture.
History Of DES
DES Originated From An Encryption Algorithm Developed By IBM In The 1970s. IBM's Work Was Influenced By Earlier Cryptographic Research And Eventually Resulted In The Algorithm Known As Lucifer. The United States National Bureau Of Standards, Now Known As The National Institute Of Standards And Technology (NIST), Sought A Standardized Encryption Algorithm For Protecting Unclassified Government Information. After Evaluation And Modification, The Algorithm Was Adopted As A Federal Standard In 1977.
DES As A Symmetric Encryption Algorithm
DES Belongs To The Category Of symmetric-key Cryptography. In Symmetric Cryptography, The Sender And Receiver Use A Shared Secret Key. The Sender Uses The Key To Encrypt Plaintext, While The Receiver Uses The Same Key To Recover The Plaintext. This Differs From Asymmetric Cryptography, Where Separate Public And Private Keys Are Used. The Main Challenge With Symmetric Encryption Is Securely Distributing And Managing The Shared Secret Key.
Block Cipher Classification
DES Is Specifically A block Cipher. Rather Than Processing An Entire Message As One Continuous Stream, DES Divides The Plaintext Into Fixed-size Blocks. Each Block Contains 64 Bits. The Cipher Then Transforms Each 64-bit Plaintext Block Into A 64-bit Ciphertext Block Using A Secret Key. If A Message Is Larger Than 64 Bits, It Is Divided Into Multiple Blocks And Processed According To A Selected Mode Of Operation.
DES Key Size
DES Is Commonly Described As Using A 64-bit Key, But Only 56 Bits Are Actually Used For Cryptographic Operations. The Remaining Eight Bits Are Parity Bits, With One Parity Bit Associated With Each Group Of Eight Key Bits. Consequently, The Effective Key Space Contains 2562^{56} Possible Keys. This Was Considered Sufficiently Large When DES Was Introduced, But Advances In Computing Power Eventually Made Exhaustive Key Searching Practical.
DES Block Size
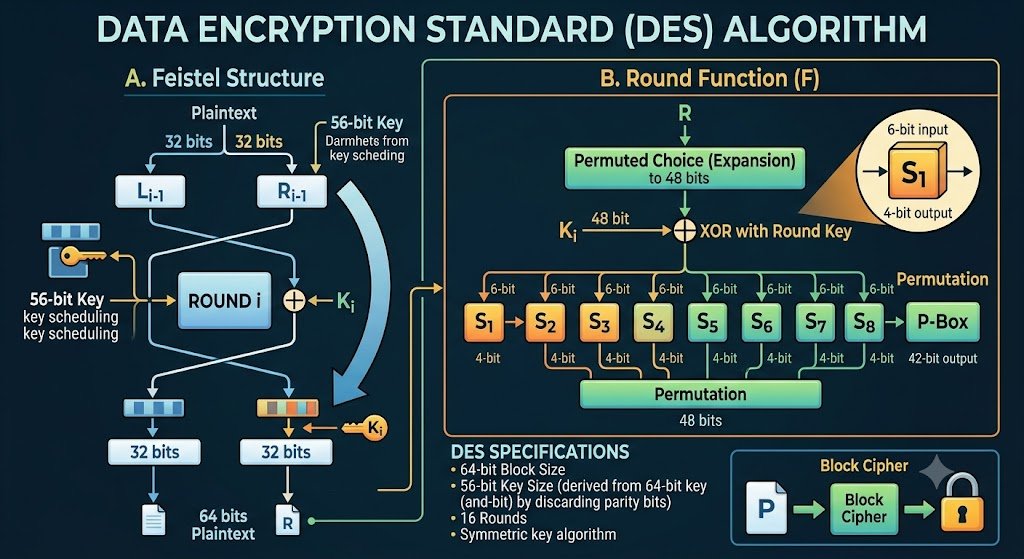
The DES Block Size Is 64 Bits, Or 8 Bytes. Every Plaintext Block Processed By The Basic DES Algorithm Therefore Contains Exactly 64 Bits. A Block Is Divided Internally Into Two 32-bit Halves Called The left Half (L) And right Half (R). These Halves Are Repeatedly Transformed During The Algorithm's 16 Encryption Rounds.
Basic DES Encryption Structure
DES Follows A Feistel Network Structure. A Feistel Network Divides The Input Block Into Two Halves And Repeatedly Applies A Transformation To One Half Using A Round Key And An Encryption Function. The Result Is Combined With The Other Half, After Which The Halves Are Exchanged. One Major Advantage Of The Feistel Structure Is That Encryption And Decryption Use Essentially The Same Algorithm, With The Round Keys Applied In Reverse Order During Decryption.
Overall DES Encryption Process
The DES Encryption Process Can Be Divided Into Several Major Stages. First, A 64-bit Plaintext Block Undergoes An Initial Permutation (IP). The Resulting Block Is Divided Into Two 32-bit Halves. These Halves Pass Through 16 Feistel Rounds. After The Sixteenth Round, The Two Halves Are Combined In A Specific Order And Passed Through The Final Permutation (FP). The Resulting 64-bit Value Is The Ciphertext.
Initial Permutation
The Initial Permutation Is The First Major Transformation Performed By DES. It Rearranges The 64 Bits Of The Plaintext According To A Fixed Permutation Table. The Permutation Does Not Add Secrecy By Itself Because The Table Is Publicly Known. Its Purpose Is Primarily Related To The Structure Of The Original DES Design And Hardware Implementation. After The Permutation, The Output Is Divided Into A 32-bit Left Half And A 32-bit Right Half.
The 16 DES Rounds
The Core Of DES Consists Of 16 Rounds. Each Round Uses A Different 48-bit Subkey Derived From The Original 56-bit Effective Key. During Each Round, The Right Half Is Expanded, Combined With The Round Key, Substituted Through S-boxes, Permuted, And Finally XORed With The Left Half. The Resulting Values Form The Input For The Next Round. Repeating This Process Provides Substantial Diffusion And Confusion.
Feistel Round
For A Particular Round ii, The DES Transformation Can Be Represented Conceptually As:
Li=Ri−1
and
Ri=Li−1⊕f(Ri−1,Ki)
where KiK_i Is The Round Key And ff Is The DES Round Function. This Structure Means That One Half Is Processed While The Other Half Is Carried Forward. The XOR Operation Ensures That Changes In One Portion Influence Subsequent Processing.
Expansion Permutation
The DES Right Half Initially Contains 32 Bits. However, The Round Key Contains 48 Bits. Therefore, DES Must Expand The 32-bit Right Half To 48 Bits Before Combining It With The Round Key. This Is Performed Using The Expansion Permutation, Commonly Called The E-box. Some Bits Are Repeated During Expansion. The Resulting 48-bit Value Is Then XORed With The 48-bit Round Key.
XOR With The Round Key
After Expansion, The 48-bit Result Is Combined With The Corresponding 48-bit Subkey Using The exclusive OR (XOR) Operation. XOR Is Fundamental To Many Cryptographic Algorithms Because It Provides An Efficient Way To Combine Data With Key Material. If A Plaintext Bit And Key Bit Are Equal, The XOR Result Is 0; If They Differ, The Result Is 1. This Operation Contributes To The Dependence Of Ciphertext On The Secret Key.
S-Boxes In DES
The Output Of The XOR Operation Contains 48 Bits. These Bits Are Divided Into Eight Groups Of Six Bits. Each Six-bit Group Is Processed By One Of DES's eight S-boxes. Each S-box Converts Six Input Bits Into Four Output Bits. Therefore, The Eight S-boxes Collectively Transform The 48-bit Input Into A 32-bit Output. S-boxes Are Among The Most Important Components Of DES Because They Introduce Nonlinear Transformations.
Importance Of S-Boxes
S-boxes Provide confusion, An Important Cryptographic Property Identified By Claude Shannon. Confusion Makes The Relationship Between The Secret Key, Plaintext, And Ciphertext Difficult To Analyze. Without Nonlinear Substitution, An Encryption Algorithm Could Potentially Be Vulnerable To Mathematical Analysis. The Design Of DES S-boxes Has Been Extensively Studied, Particularly In Relation To Differential And Linear Cryptanalysis.
P-Box Permutation
After S-box Substitution, DES Produces 32 Bits. These Bits Are Rearranged Using Another Fixed Permutation Called The P-box Or Permutation Box. The P-box Changes The Positions Of The S-box Outputs So That Bits Originating From Different S-boxes Influence Different Portions Of Subsequent Rounds. This Helps Create Diffusion Throughout The Encrypted Data.
DES Round Function
The DES Round Function Can Therefore Be Summarized As Four Major Operations: expansion, Key Mixing, Substitution, And Permutation. The 32-bit Right Half Is Expanded To 48 Bits, XORed With A 48-bit Round Key, Processed Through Eight S-boxes, And Finally Passed Through The P-box. The Resulting 32-bit Value Is XORed With The Left Half. This Complete Operation Forms One Feistel Round.
Key Generation In DES
DES Requires 16 Different Round Keys. These Are Generated From The Original 64-bit Key, Of Which 56 Bits Are Effective. First, The Key Passes Through A Permutation Called PC-1 (Permuted Choice 1). This Removes The Eight Parity Bits And Rearranges The Remaining 56 Bits. The Resulting Key Is Divided Into Two 28-bit Halves, Usually Called C0C_0 And D0D_0.
Key Shifts
During Each DES Round, The Two 28-bit Key Halves Undergo Circular Left Shifts. Depending On The Round, Either One-bit Or Two-bit Shifts Are Performed. The Shifted Halves Are Then Combined And Processed Using Another Permutation Known As PC-2 (Permuted Choice 2). PC-2 Selects 48 Bits From The Combined 56-bit Value To Create The Round Key. This Process Is Repeated For All 16 Rounds.
DES Key Schedule
The Complete Process Of Producing The 16 Round Keys Is Called The DES Key Schedule. It Ensures That Different Rounds Use Different Portions And Arrangements Of The Original Key. The Sequence Of Round Keys Contributes To DES's Security By Preventing All Rounds From Using Identical Key Material. During Decryption, The Same Key Schedule Can Be Used, But The Generated Round Keys Are Applied In The Reverse Order.
Final Permutation
After The Sixteenth Feistel Round, DES Performs A Final Rearrangement. The Two Resulting 32-bit Halves Are Combined In Reverse Order, And The Combined 64-bit Block Is Passed Through The Final Permutation (FP). The Final Permutation Is Effectively The Inverse Of The Initial Permutation. The Resulting 64-bit Block Is The DES Ciphertext.
DES Decryption
One Elegant Feature Of DES Is That Decryption Uses The Same Fundamental Structure As Encryption. The Primary Difference Is The Order Of The Round Keys. During Encryption, The Keys Are Applied As K1, K2,…, K16. During Decryption, They Are Applied As K16, K15, …, K1. This Property Is A Direct Benefit Of The Feistel Network Design.
Simple DES Encryption Flow
A Simplified DES Encryption Flow Can Be Represented As:
Plaintext (64 Bits)
↓
Initial Permutation
↓
32-bit L + 32-bit R
↓
16 Feistel Rounds
↓
Swap Halves
↓
Final Permutation
↓
Ciphertext (64 Bits)
The Corresponding Decryption Process Reverses The Round-key Sequence And Recovers The Original Plaintext.
Avalanche Effect
DES Demonstrates An Important Cryptographic Characteristic Called The avalanche Effect. A Small Change In The Plaintext Or Encryption Key Should Cause Significant Changes In The Resulting Ciphertext. Ideally, Changing A Single Input Bit Should Eventually Affect Approximately Half Of The Ciphertext Bits. This Property Makes It Difficult For Attackers To Predict How Changes In Plaintext Will Influence Encrypted Output.
Confusion And Diffusion
DES Was Designed Around Two Important Principles: confusion And Diffusion. Confusion Makes The Relationship Between The Key And Ciphertext Complex, Primarily Through S-box Substitution. Diffusion Spreads The Influence Of Individual Plaintext Bits Throughout The Ciphertext, Supported By Permutations, Expansion, And Repeated Feistel Rounds. Together, These Principles Make Statistical Analysis Of The Encrypted Data More Difficult.
DES Modes Of Operation
DES By Itself Encrypts Individual 64-bit Blocks. To Securely Encrypt Longer Messages, A mode Of Operation Is Required. Historically, DES Was Used With Modes Such As Electronic Codebook (ECB), Cipher Block Chaining (CBC), Cipher Feedback (CFB), And Output Feedback (OFB). Each Mode Changes How Individual Blocks Are Processed. Modern Cryptographic Systems Generally Avoid DES Because The Underlying Key Size Is No Longer Considered Secure.
Electronic Codebook Mode
In ECB Mode, Each Plaintext Block Is Encrypted Independently Using The Same DES Key. Although This Is Simple, It Has A Serious Weakness: Identical Plaintext Blocks Produce Identical Ciphertext Blocks. Consequently, Patterns Within Structured Data Can Remain Visible. ECB Is Therefore Generally Unsuitable For Encrypting Large Structured Messages, Even When Used With Algorithms That Have Stronger Keys.
Cipher Block Chaining Mode
CBC Mode Improves Upon ECB By Linking Each Plaintext Block With The Previous Ciphertext Block Before Encryption. The First Block Uses An Initialization Vector (IV). This Means Identical Plaintext Blocks Can Produce Different Ciphertext Depending On Their Position And Preceding Data. CBC Was Historically Important In DES-based Systems, But Modern Applications Generally Use Authenticated Encryption Algorithms Rather Than Legacy DES-CBC.
Security Of DES
The Primary Security Weakness Of DES Is Its 56-bit Effective Key Size. The Number Of Possible Keys Is:
256 = 72, 057, 594, 037, 927, 936
Although This Appears Extremely Large, Modern Specialized Hardware Can Search Enormous Numbers Of Keys. In 1998, The Electronic Frontier Foundation Demonstrated That A DES Key Could Be Recovered Through A Dedicated Brute-force Machine In A Matter Of Days. This Demonstrated That DES's Key Length Was No Longer Adequate For Serious Security Applications.
Brute-Force Attacks
A brute-force Attack Attempts To Test Possible Keys Until The Correct Key Is Discovered. Because DES Has Only 56 Effective Key Bits, An Attacker Can Theoretically Test Every Possible Key. The Expected Number Of Attempts Is Approximately Half The Total Key Space, Although Practical Attack Times Depend On Hardware, Implementation, And Available Ciphertext/plaintext Information.
Cryptanalysis Of DES
Besides Brute-force Attacks, Researchers Have Studied DES Using Advanced Cryptanalytic Techniques. Differential Cryptanalysis Examines How Differences In Plaintext Can Influence Differences In Ciphertext. Linear Cryptanalysis Attempts To Identify Statistical Relationships Between Plaintext, Ciphertext, And Key Bits. DES Was Designed With Considerable Resistance To These Techniques, Although Its Relatively Small Key Size Ultimately Became Its Most Significant Practical Weakness.
Triple DES
To Extend The Useful Life Of DES, Triple DES (3DES Or TDEA) Was Introduced. Instead Of Applying DES Only Once, Triple DES Applies DES Three Times.
A Common Arrangement Is Encrypt-Decrypt-Encrypt (EDE):
C=EK3(DK2(EK1(P)))
Depending On The Key Configuration, Triple DES Can Provide Substantially Greater Security Than Ordinary DES. However, It Remains Based On A 64-bit Block Size And Is Much Slower Than Modern Algorithms Such As AES.
DES Versus AES
The Advanced Encryption Standard (AES) Replaced DES As The Preferred Modern Symmetric Encryption Standard. AES Supports Key Sizes Of 128, 192, And 256 Bits And Uses A 128-bit Block Size. Compared With DES, AES Provides Significantly Stronger Security And Better Performance On Modern Systems. DES Remains Valuable For Historical And Educational Purposes, While AES Is Generally Preferred For Contemporary Applications.
Advantages Of DES
DES Has Several Historical And Educational Advantages. Its Feistel Structure Is Relatively Easy To Understand And Provides A Clear Example Of How Block Ciphers Operate. Encryption And Decryption Use The Same Fundamental Structure, Simplifying Implementation. DES Was Also Standardized And Extensively Analyzed By Researchers Worldwide. Its Widespread Historical Adoption Helped Establish Important Practices In Modern Symmetric Cryptography.
Disadvantages Of DES
The Most Important Disadvantage Of DES Is Its short 56-bit Effective Key. It Is Vulnerable To Brute-force Key-search Attacks And Should Not Be Used To Protect Sensitive Modern Information. Its 64-bit Block Size Is Also Small By Current Standards, And Legacy DES Modes Can Have Additional Weaknesses. Furthermore, DES Is Inefficient Compared With Modern Algorithms And Has Been Superseded By Stronger Standards.
Historical Applications Of DES
DES Was Widely Used In Banking, Financial Systems, Government Systems, Telecommunications, And Commercial Software. One Notable Historical Application Was The Protection Of Financial Transactions And ATM-related Systems. DES Also Influenced The Development Of Later Financial Cryptographic Standards. Although Most Modern Systems Have Moved Away From DES, Its Historical Impact On Computer Security And Cryptographic Engineering Remains Significant.
Importance Of DES In Cryptography Education
DES Continues To Be Taught Because It Provides An Excellent Case Study Of Block-cipher Design. Students Can Learn About Permutations, Substitution, XOR Operations, S-boxes, P-boxes, Key Schedules, Feistel Networks, Avalanche Effects, And Cryptanalysis Through One Algorithm. Understanding DES Also Makes It Easier To Understand Why Modern Algorithms Require Larger Keys, Stronger Security Margins, And Better Block Sizes.
Modern Status Of DES
DES Should Now Be Regarded Primarily As A legacy Cryptographic Algorithm. It Is Not Appropriate For New Security Applications Because Its Effective Key Length Is Insufficient Against Modern Brute-force Capabilities. Organizations Maintaining Old Systems Should Migrate To Modern Cryptographic Standards. AES Is The Usual Replacement For General-purpose Symmetric Encryption, While Authenticated Encryption Schemes Such As AES-GCM Are Preferred When Both Confidentiality And Integrity Are Required.
Summary Of DES
In Summary, DES Is A 64-bit Block Cipher Based On A 16-round Feistel Network. It Uses A 56-bit Effective Key Derived From A 64-bit Key Containing Parity Bits. Its Major Components Include The Initial Permutation, Expansion Function, XOR Key Mixing, Eight S-boxes, P-box Permutation, 16-round Key Schedule, And Final Permutation. DES Introduced And Popularized Concepts That Remain Fundamental To Modern Cryptography, Even Though Its Security Is No Longer Adequate.
Conclusion
The Data Encryption Standard (DES) Represents An Important Milestone In The History Of Computer Security. It Demonstrated How A Carefully Designed Symmetric Block Cipher Could Provide Practical Confidentiality For Large-scale Computing Systems. However, Technological Advances Eventually Made Its 56-bit Key Vulnerable To Brute-force Attacks. DES Has Therefore Been Replaced By Stronger Algorithms Such As AES. Nevertheless, Studying DES Remains Highly Valuable For Understanding Block Ciphers, Feistel Networks, Cryptographic Key Schedules, S-boxes, Permutations, Diffusion, Confusion, Avalanche Effects, And The Evolution Of Modern Encryption Technology.
Tags:
Data Encryption Standard, History Of DES, Block Cipher Classification, S-Boxes In DES, P-Box Permutation, DES Decryption